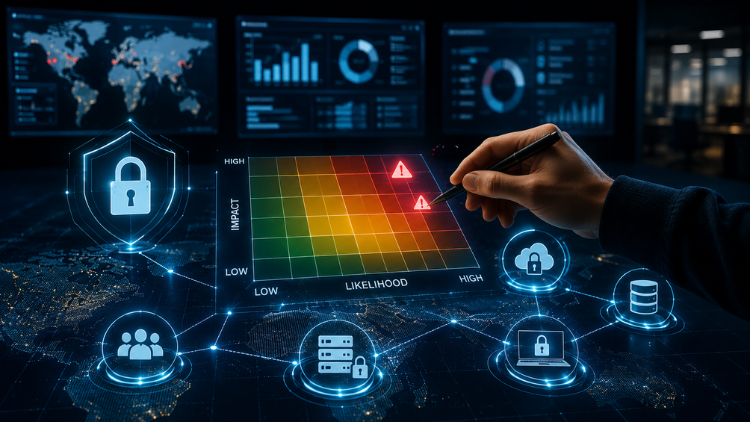
Explore how a logarithmic likelihood scale converts event frequency into scale values to quantify information security risk and prioritize actions, with examples from data breaches, unauthorized access, and regulatory risks.
ISO 27005:2022: Information Security Risk Management (Khóa học)
Risk Identification, Analysis, Evaluation, Treatment & Acceptance | Context, Criteria & Monitoring
Tất cả các cấp độ • 48 Bài giảng • Truy cập trọn đời
Giảng viên chính đã được xác minh
ĐOẠN PHIM GIỚI THIỆU
Gặp người hướng dẫn của bạn: Dr. Amar Massoud
18 ms
5.0 / 5.0
Đánh giá toàn cầuTiếng Anh (Mỹ)
99 ngôn ngữ phụ đề4 giờ 25 phút
Tổng số nội dungBạn sẽ học được gì
Understand and apply ISO 27005:2022 methodologies for information security risk assessments.
Identify, analyze, and evaluate risks to information security within an organizational context.
Develop and implement effective risk treatment plans aligned with ISO 27005:2022 guidelines.
Continuously monitor and review risk management processes for ongoing improvement and compliance.
Nội dung khóa học
8 phần • 48 bài giảng • 04:25:24 tổng chiều dàiQualitative Risk Assessment Approach
02:52
Consequence Criteria
06:38
Qualitative Consequence Scale
05:42
Likelihood Criteria
03:02
Qualitative Likelihood Scale
05:18
Criteria for Determining the Level of Risk
02:42
Qualitative Level of Risks
05:30
Choosing an Appropriate Method
03:02
Information Security Risk Assessment Process
03:42
Risk Assessment Methodologies
08:09
Identifying Information Security Risks
04:46
Asset Based Risk Identification
04:58
Identify Vulnerabilities and Threats
08:54
HealthSecure Assets Risk Identification
02:11
Identifying Risk Owners
03:22
Analysing Information Security Risks
02:45
Assessing Potential Consequences
05:28
Assess consequences of information security risks under ISO 27005:2022 by analyzing risk scenarios, evaluating confidentiality, integrity, and availability impacts, reviewing controls, and guiding risk mitigation.
Assessing Likelihood
06:34
Determining the Level of Risks
05:26
Determine risk levels in ISO 27005:2022 through a process that combines likelihood and consequences to rank risks for treatment decisions, including EHR software and cloud servers.
Prioritizing the Analyzed Risks for Risk Treatment
03:27
Event Based Risk Identification
09:32
Information Security Risk Treatment
11:16
Producing the Statement of Applicability
05:43
Information Security Risk Treatment Plan
08:44
Residual Risks
05:18
Kế Hoạch Học Hàng Tuần
Lên kế hoạch học tập của bạn
AI tạo lịch trình cá nhân theo thời gian của bạn5 giờ/tuần
Yêu cầu
This course is designed to be accessible to beginners. No advanced technical knowledge is required.
Basic familiarity with information security concepts will be helpful but not essential.
The course will cover foundational elements, making it suitable for those new to risk assessment in the context of ISO standards.
Đối tượng mục tiêu
Information Security Professionals: Ideal for security analysts, managers, and consultants seeking to deepen their understanding of risk assessment aligned with ISO standards.
IT Professionals: IT staff responsible for managing and safeguarding digital assets, especially those involved in developing or maintaining an Information Security Management System.
Compliance Officers and Auditors: Professionals ensuring regulatory compliance or conducting internal audits, particularly in sectors with strict data protection requirements.
Business Managers and Executives: Decision-makers who need to understand organizational risk landscapes and make informed information security investment decisions.
Về khóa học này
Course Overview: Dive into the world of risk assessment in line with ISO/IEC 27005:2022 standards in our comprehensive course. This training is uniquely designed to provide a blend of theoretical knowledge and practical application, using a fictional model company, "HealthSecure Inc.," as a continuous case study throughout the course.
What You'll Learn:
- Fundamentals of ISO 27005:2022: Understand the core concepts, principles, and frameworks of ISO 27005:2022.
- Risk Assessment Techniques: Learn to identify, analyze, and evaluate information security risks using proven methodologies.
- Practical Application: Apply your learning to real-life scenarios through the HealthSecure Inc. case study, encompassing various aspects of risk assessment and treatment.
- Use of Tools and Templates: Gain hands-on experience with risk assessment tools and templates that can be adapted to your professional context.
- Interactive Learning: Engaging content including lectures, interactive sessions, and group discussions.
- HealthSecure Inc. Case Study: A comprehensive use case running throughout the course, providing practical insights into the application of risk assessment in a business environment.
- Hands-On Assignments: Practical assignments and projects that simulate real-world risk assessment challenges.
- Resource Toolkit: Access to a range of templates and tools for conducting risk assessments, allowing for immediate application in your workplace.
- Expert Instructors: Learn from experienced professionals with extensive knowledge in information security and risk management.
Cơ hội Nghề nghiệp & Vị trí Mục tiêu
Xây dựng kỹ năng thực tế sẵn sàng làm việc và ứng tuyển vào các vị trí được săn đón
Chương trình Sẵn sàng Làm việc
Vị trí Công việc Bạn có thể Ứng tuyển
Full Stack Software Engineer
Backend Systems Developer
Frontend Application Specialist
Automation & Scripting Engineer
Mức Lương Ước tính Hàng năm
$90,000 – $145,000 / yr
Nhu cầu Thị trường Toàn cầu
High Global Tech Demand
Kỹ năng Nòng cốt Bạn sẽ Nắm vững* Ước tính dựa trên tiêu chuẩn tuyển dụng công nghệ toàn cầu.
Production Code Architecture
RESTful & Modern API Design
State Management & UI Scaling
Debugging & Automated Testing
Gặp gỡ giảng viên của bạn
Dr. Amar Massoud
Giảng viên chính
PhD in computer science and IT manager with 36 years technical experience in various fields including IT Security, IT Governance, IT Service Management , Software Development, Project Management, Business Analysis and Software Architecture. I hold 80+ IT certifications such as :
ITIL 4 Master, ITIL 3 Expert
ISO 27001 Auditor, ComptIA Security+, GSEC, CEH, ECSA, CISM, CISSP, CISA
PGMP, MSP
PMP, PMI-ACP, Prince2 Practitioner, Praxis, Scrum Master
COBIT 2019 Implementor, COBIT 5 Assessor/Implementer
TOGAF certified
Lean Specialist, VSM Specialist
PMI RMP, ISO 31000 Risk Manager, ISO 22301 Lead Auditor
PMI-PBA, CBAP
Lean Six Sigma Black Belt, ISO 9001 Implementer
Azure Administrator, Azure DevOps Expert, AWS Practitioner
And many more....
Sinh viên cũng mua
Những người học đã xem khóa học này cũng đã đăng ký vào các khóa học được xếp hạng hàng đầu này

Bán chạy nhất
MIỄN PHÍ
CNTT & Phần mềm | Phần cứngTiếp tục học
Program ESP32 Board without writing a single code in A Professional Environment
5.0
2 giờ 30 phút
18 Tất cả
Tất cả các cấp độ
Tiếp tục học

CNTT & Phần mềm | Phần cứng
Revolutionize Your Coding Skills with Al: A Comprehensive Guide for Beginners
5.0
2 giờ
11 Tất cả
Tất cả các cấp độ
$10.99
$19.99

CNTT & Phần mềm | Bảo mật thông tin
Master ISO 27001: Achieve Certification, Build Security, and Ensure Compliance for Your Organization
5.0
1 giờ 30 phút
10 Tất cả
Người mới bắt đầu
$39.99
$54.99

CNTT & Phần mềm | Được chứng nhận về Quản trị, Rủi ro và Tuân thủ (CGRC)
Master GRC: Step-by-Step Guide to Implementing Governance, Risk, and Compliance for Business Success
5.0
2 giờ 30 phút
35 Tất cả
Trung cấp
$39.99
$64.99

CNTT & Phần mềm | Arduino
Seamlessly Stream and Visualize Real-Time Data from Arduino into Excel with Ease
5.0
1 giờ 30 phút
6 Tất cả
Tất cả các cấp độ
$9.99
$34.99

CNTT & Phần mềm | CNTT & Phần mềm khác
Learn how to create and customize a website with no prior coding experience.
5.0
1 giờ 30 phút
12 Tất cả
Tất cả các cấp độ
$9.99
$19.99
Câu hỏi thường gặp
Tìm câu trả lời cho những câu hỏi phổ biến nhất về khóa học này.
Đúng! Sau khi hoàn thành 100% các bài giảng và bài tập của khóa học, bạn có thể tải xuống ngay Chứng chỉ Hoàn thành kỹ thuật số đã được xác minh trực tiếp từ hồ sơ Lucebra của mình.
Khám phá thêm trong Technology
Mở rộng hành trình học tập với chứng chỉ uy tín, sách điện tử liên quan và lớp học trực tiếp tương tác.